Key Takeaways
- EU Cyber Resilience Act reporting requirements took effect on Sept. 11, putting manufacturers of digital products.
- Companies must issue an early warning within 24 hours after becoming aware of an actively exploited vulnerability or severe security incident.
- Breaching the Cyber Resilience Act can expose companies to fines of up to €15 million or 2.5% of worldwide annual turnover.
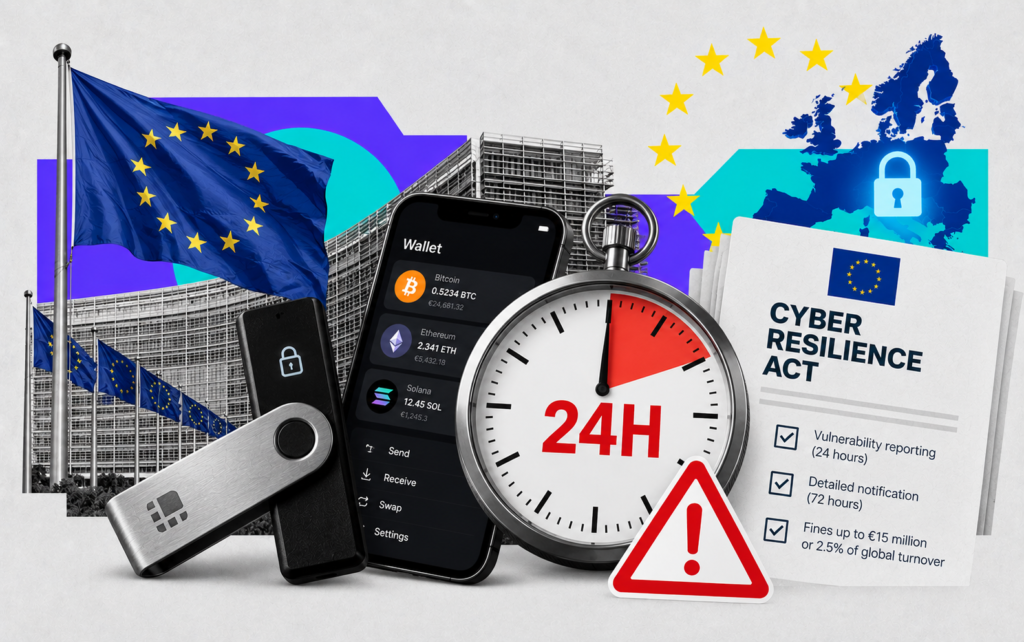
Crypto wallet makers operating in the European Union now face a 24-hour clock to report actively exploited security vulnerabilities as a major part of the bloc’s Cyber Resilience Act (CRA) comes into force.
The reporting requirements became applicable on Sept. 11, 2026, extending the EU’s cybersecurity oversight across products containing digital elements.
That potentially brings hardware wallets, wallet applications and other crypto-related software products within the framework when they meet the CRA’s scope.
The rules arrive as cyber risk remains a growing concern for European regulators.
The European Securities and Markets Authority (ESMA) warned last week that operational risks across financial markets were at a “very high level and rising,” pointing partly to cyber threats and advances in artificial intelligence.
Crypto Wallet Makers Face a 24-Hour Clock
Under the CRA, manufacturers must submit an early warning within 24 hours of becoming aware of an actively exploited vulnerability or severe security incident affecting a covered product.
A more detailed notification is then required within 72 hours.
For exploited vulnerabilities, manufacturers must also provide a final report no later than 14 days after a corrective or mitigating measure becomes available. Severe incidents require a final report within one month of the 72-hour notification.
Reports are submitted through the CRA Single Reporting Platform established by the European Union Agency for Cybersecurity (ENISA), which became operational alongside the reporting rules on Sept. 11.
Importantly, the requirements can cover products already on the EU market, rather than applying only to products launched after the new rules took effect.
Fines Can Reach €15 Million
The financial consequences could be significant.
Violations of key CRA cybersecurity obligations can carry administrative fines of up to €15 million ($17.3 million) or 2.5% of a company’s total worldwide annual turnover from the preceding financial year, whichever is higher.
That makes the regime particularly relevant to major wallet manufacturers and software providers serving EU customers.
However, the CRA is broader than crypto regulation. It covers connected hardware and software products ranging from consumer applications and smart devices to security products.
The European Commission says its goal is to make manufacturers responsible for cybersecurity throughout a product’s lifecycle.
EU Tightens Crypto Cybersecurity Net
For crypto companies, the CRA adds another layer to an increasingly dense European regulatory framework.
Crypto-asset service providers are already subject to the EU’s Markets in Crypto-Assets Regulation (MiCA), while financial entities covered by the Digital Operational Resilience Act (DORA) face separate requirements for managing and reporting major ICT incidents.
DORA’s reporting framework can similarly require an initial notification no later than 24 hours after an entity becomes aware of an incident.
The CRA changes the equation for wallet security by focusing directly on the products themselves.
For wallet providers, discovering an actively exploited vulnerability is therefore no longer simply a race to patch users’ software or firmware. In the EU, it can also start a regulatory countdown measured in hours.
The information provided in this article is for informational purposes only. It is not intended to be, nor should it be construed as, financial advice. We do not make any warranties regarding the completeness, reliability, or accuracy of this information. All investments involve risk, and past performance does not guarantee future results. We recommend consulting a financial advisor before making any investment decisions.

Giuseppe Ciccomascolo began his career as an investigative journalist in Italy, where he contributed to both local and national newspapers, focusing on various financial sectors.
Upon relocating to London, he worked as an analyst for Fitch's CapitalStructure and later as a Senior Reporter for Alliance News. In 2017, Giuseppe transitioned to covering cryptocurrency-related news, producing documentaries and articles on Bitcoin and other emerging digital currencies. He also played a pivotal role in establishing the academy for a cryptocurrency exchange website. Crypto remained his primary area of interest throughout his tenure as a writer for ThirdFloor.